Cybersecurity does not start with complex tools
As developers, it is easy to associate cybersecurity with highly technical topics such as encryption, penetration testing, infrastructure or threat detection.
However, a large part of security begins with correctly applying fundamental principles.
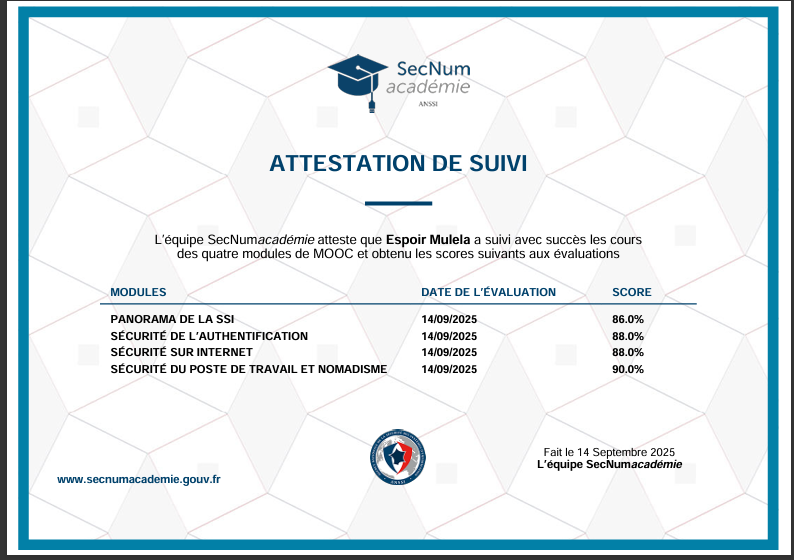
That is the perspective from which I completed the SecNumAcadémie programme offered by ANSSI.
A programme structured around four modules
The training covers four complementary areas:
- Information systems security overview
- Authentication security
- Internet security
- Workstation security and remote working
I completed all four modules in September 2025.
Beyond the certificate itself, the programme helped me better structure my understanding of risks related to access, digital usage and workstation protection.
A direct connection with software development
Even when cybersecurity is not your primary specialization, these principles directly influence how applications should be designed.
In my projects, this connects with topics such as:
- authentication;
- authorization;
- data protection;
- access management;
- HTTPS communications;
- API security;
- production environment configuration;
- secure server-side practices.
Security should not be something added at the end of a project.
It should be considered from the beginning of the design process.
What I take away from the experience
This training reinforced the idea that reliable systems depend not only on technical choices, but also on consistently applying good security practices.
For me, it is a foundation that I intend to keep strengthening through my projects, deployments and professional development.